What Should a Small Business Do After a Cyber Attack?

After a cyber attack, a small business should isolate affected systems, preserve evidence, contact its IT or security response team and protect important accounts. Record what happened, assess whether personal data was affected and consider reporting duties. Restore services only after checking the cause and the safety of backups.
Key takeaways
- Isolate affected systems and preserve evidence.
- Use a trusted channel to activate your incident response plan.
- Assess ICO and other notification duties promptly.
- Restore only after investigating the cause and validating backups.
What should you do in the first 15 minutes?
Stop using affected devices and disconnect them from networks if your response plan instructs you to do so. Do not erase or reset them without advice, because logs and other evidence may be lost.
Contact the person responsible for incident response. If you use an external IT provider, tell them what you saw, when it started and which systems appear affected.
Use a trusted telephone number or separate communication channel if company email may have been compromised. Ask colleagues not to forward suspicious files or attempt their own fixes.
How do you contain a cyber attack without making it worse?
Containment means limiting further damage while preserving the information needed to understand the incident. It may involve disabling accounts, revoking sessions, isolating endpoints or temporarily blocking access.
Avoid changing every setting at once. Record each action and time, then let a designated incident lead coordinate technical steps. If criminals claim to have stolen data, treat that as an allegation until assessed.
For ransomware, do not reconnect a device simply because a ransom screen disappears. A clean-up and recovery decision should be based on evidence, not appearance.
When must a UK business report a data breach?
A cyber attack is not automatically a reportable personal data breach. The key question is whether personal data was affected and whether the incident is likely to create a risk to people’s rights and freedoms.
Where the reporting threshold is met, the ICO says organisations must notify it without undue delay and, where feasible, within 72 hours of becoming aware. A high risk to individuals may also require informing those people without undue delay.
Keep an incident log even if reporting is not required. Record the affected information, risk assessment, containment steps and reasons for the decision. Sector regulators, insurers and customers may have separate notification rules.
Free download: get the Cyber incident response checklist to turn this advice into a repeatable process.
How can you recover operations safely?
Identify the systems your business needs first: email, customer records, finance, telephony and essential applications. Prioritise recovery according to business impact, not simply the order in which systems failed.
Before restoring backups, establish how attackers entered and check that backup copies are suitable for recovery. Rebuild compromised devices from trusted sources where appropriate, reset affected credentials and monitor for renewed activity.
Test a restored service with a small group before returning everyone to it. Tell employees what has changed and what warning signs they should report.
What should your incident response plan contain?
Keep a short plan with an incident lead, deputy, supplier contact numbers, a list of essential systems and a decision process for customer communications. Store an accessible copy outside the systems that could fail.
Define who can authorise system isolation, who speaks to customers and who checks legal or regulatory reporting. Run a short tabletop exercise twice a year and update the plan after staff or supplier changes.
A managed detection and response service can help detect suspicious activity and coordinate technical response, but it does not replace leadership decisions or legal advice.
What should you do next?
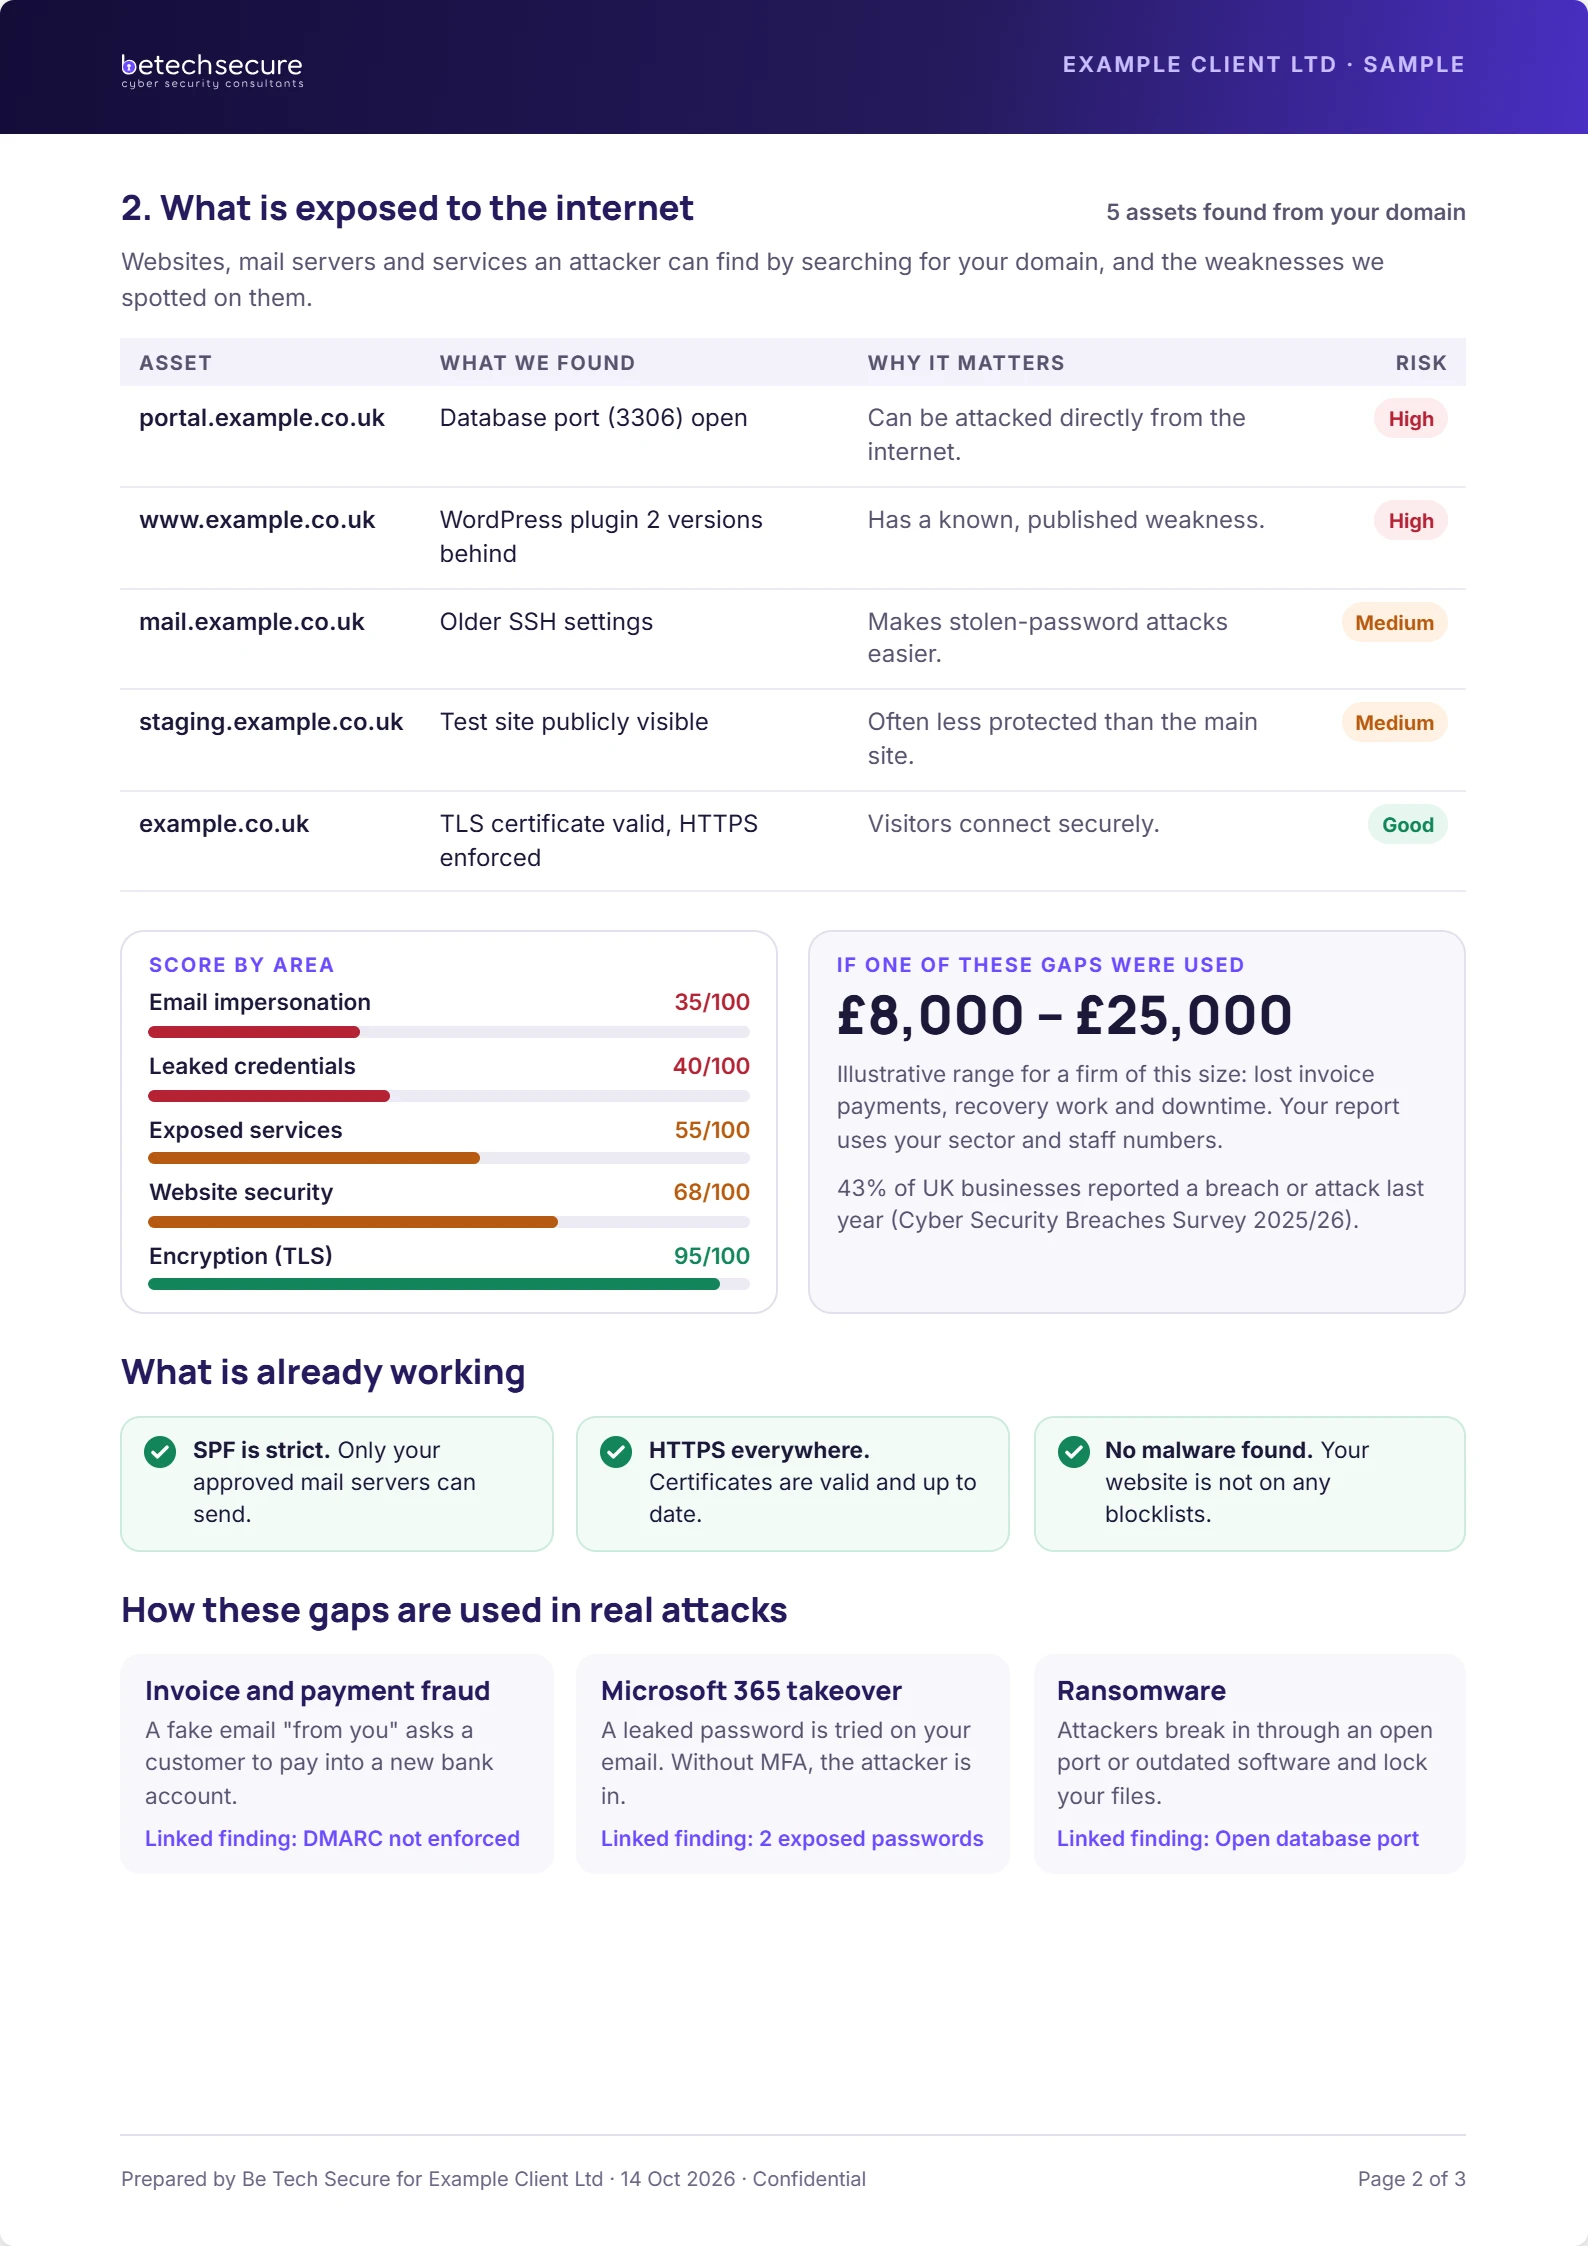
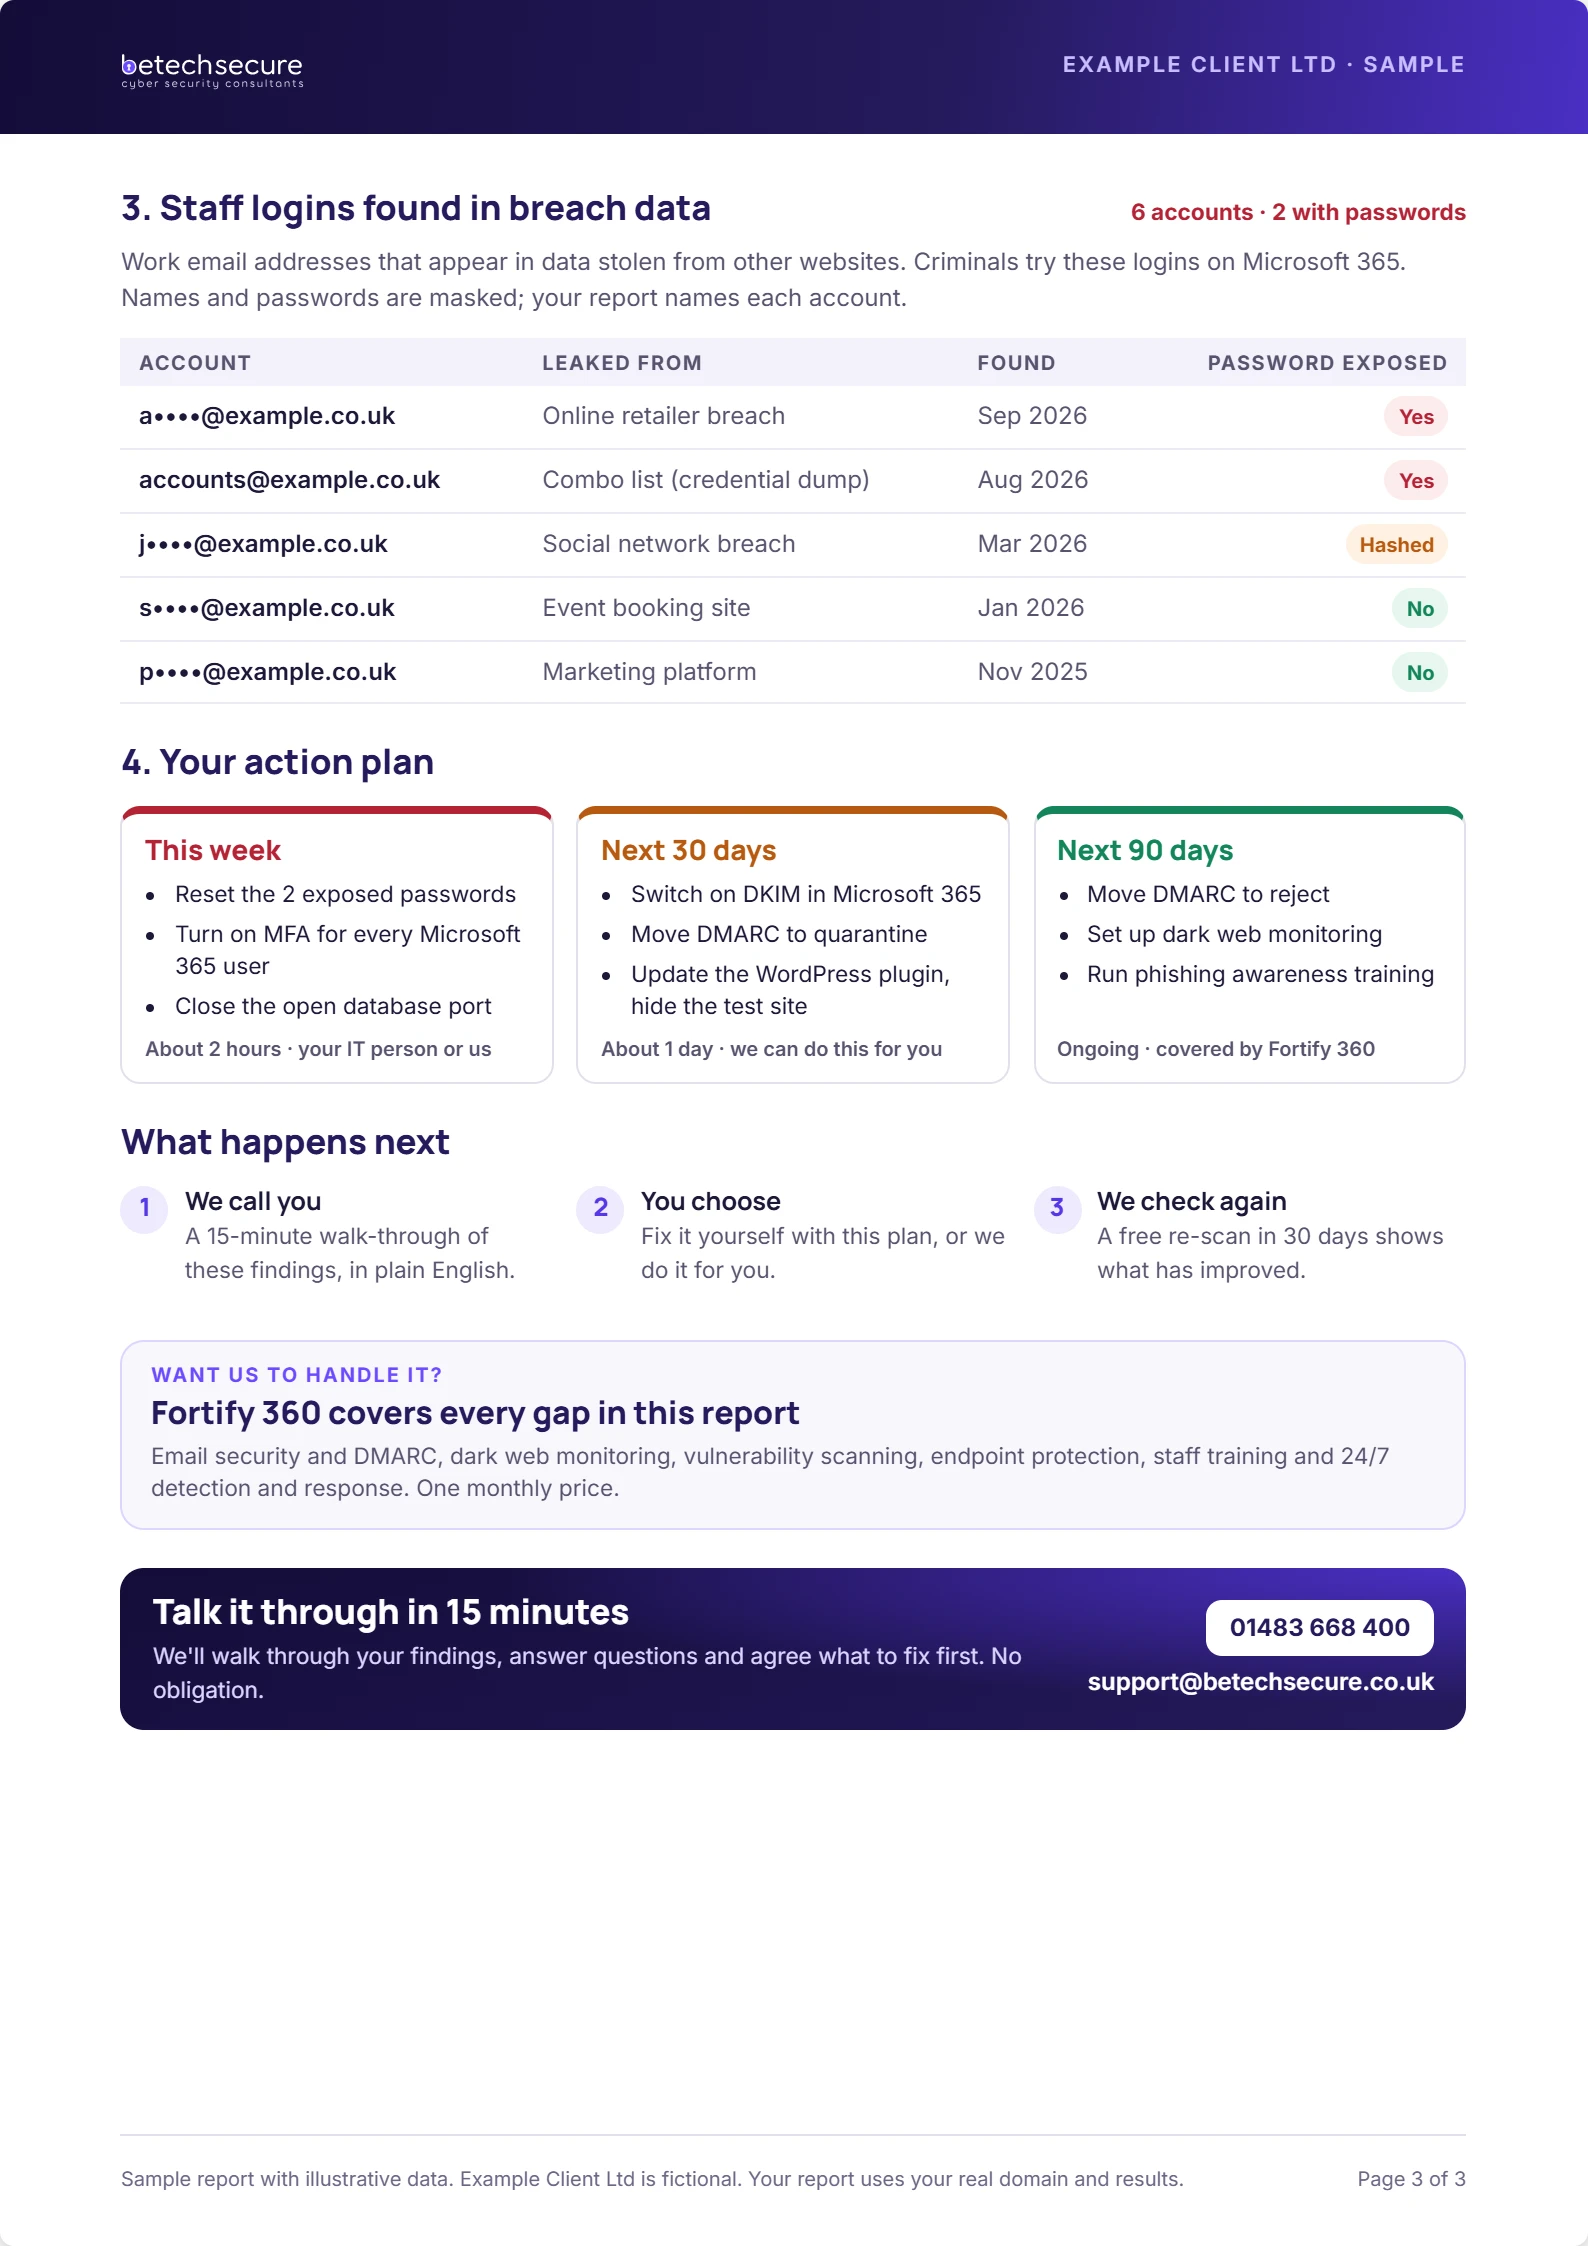
Want to know where your business is exposed? Request a free security risk review or book a 15-minute conversation with Be Tech Secure.
Frequently asked questions
Should I turn off a hacked computer?
Do not assume powering off is always the right first action. Isolation may prevent further spread, but shutting down can lose useful evidence. Follow your incident response plan and take guidance from your security specialist.
Do all cyber attacks need to be reported to the ICO?
No. ICO reporting depends on whether a personal data breach is likely to result in a risk to individuals. Keep a record of your assessment even if you decide reporting is not required.
Should a business pay a ransomware demand?
Payment does not guarantee recovery or deletion of stolen information. Seek specialist incident response and legal advice, check relevant sanctions risks and involve the appropriate authorities.
How long does recovery take?
There is no reliable universal timeframe. Recovery depends on the attack, affected systems, backup quality and investigation findings. A tested response plan can reduce uncertainty and downtime.