Penetration testing services for UK SMEs
Penetration testing for UK SMEs: find your weaknesses before attackers do.
A penetration test is an authorised, simulated cyber attack that finds the weaknesses in your systems before criminals do. Our testers show you exactly what an attacker could reach, how serious it is and how to fix it, with a report your customers, insurers and auditors will accept.
- Pass customer and tender security checks
- Evidence for insurers, ISO 27001 and auditors
- Know exactly what to fix first
- Manual testing, not just automated scans
Your testing team
Josh Ingram, Senior Security Consultant7 years' security consulting experience across finance, accounting, banking and healthcare.Trusted by UK businesses like yours
What clients say after their penetration test.
“We assumed our systems were secure because we’d never experienced a serious incident. The penetration test highlighted weaknesses we simply wouldn’t have found ourselves.”
Security vulnerabilities identified and prioritised for remediation
Oliver M.Managing Director · Financial Services, 23 staff“A client asked us to provide evidence of independent security testing before renewing our contract. We needed a proper assessment and a report we could share.”
Independent penetration test completed with documented findings
Laura S.Operations Director · Technology Services, 31 staff“We’d invested in security software but had never actually tested whether our defences would hold up. The assessment gave us a much clearer picture.”
Practical remediation plan based on independent security testing
Peter J.Director · Legal Services, 16 staff
Certifications & partnerships
Why UK businesses book a penetration test
Most SMEs come to us when something, or someone, is asking for proof.
Win and keep customer contracts
Answer tender and supplier security questions with an independent report. Need help with the questionnaire itself? Our vCISO can lead it.
Satisfy your cyber insurer
Show your controls have been independently tested, which can help with cover and premiums.
Meet ISO 27001 and audit requirements
Provide the technical testing evidence auditors expect, alongside Cyber Essentials Plus.
Get clarity after a scare
After an incident or near miss, find out what else is exposed before someone else does.
Types of penetration testing we offer
Choose the areas you need, or tell us what you're trying to protect and we'll recommend the right scope.
External infrastructure testing
Find out whether attackers could get in through your internet-facing servers, firewalls, VPNs and exposed services.
Internal network testing
See how far an attacker could get if a laptop or account were compromised, and stop them reaching your critical data.
Web application testing
Stop customer data leaking through your website, portal or app, including the OWASP Top 10 and business logic flaws.
Cloud security testing
Close the misconfigurations in Azure and AWS that expose data and systems to the internet.
Microsoft 365 security review
Lock down email, Teams, SharePoint and OneDrive settings that attackers commonly exploit.
Wireless network testing
Make sure your office Wi-Fi can't be used as a back door into your business network.
Vulnerability scan vs penetration test vs red team
A scan tells you what might be wrong. A penetration test proves what an attacker could actually do, and what to fix first. For most SMEs, it's the right level of assurance.
Get My Quote| What you get | Vulnerability scan | Penetration test | Red team |
|---|---|---|---|
| Finds known weaknesses | Yes | Yes | Yes |
| Manual testing by experts | No | Yes | Yes |
| Proves real-world impact | No | Yes | Yes |
| Accepted by customers and insurers | Sometimes | Yes | Yes |
| Best for | Ongoing hygiene | Most SMEs | Large, mature teams |
How our penetration testing works
Clear communication at every stage, and no surprises.
- 1ScopeWe agree what's tested, when, and a fixed price.
- 2TestSpecialists safely simulate real-world attacks.
- 3ReportClear findings, risk ratings and fixes, plus a debrief.
- 4RetestWe confirm the fixes worked, with updated evidence.
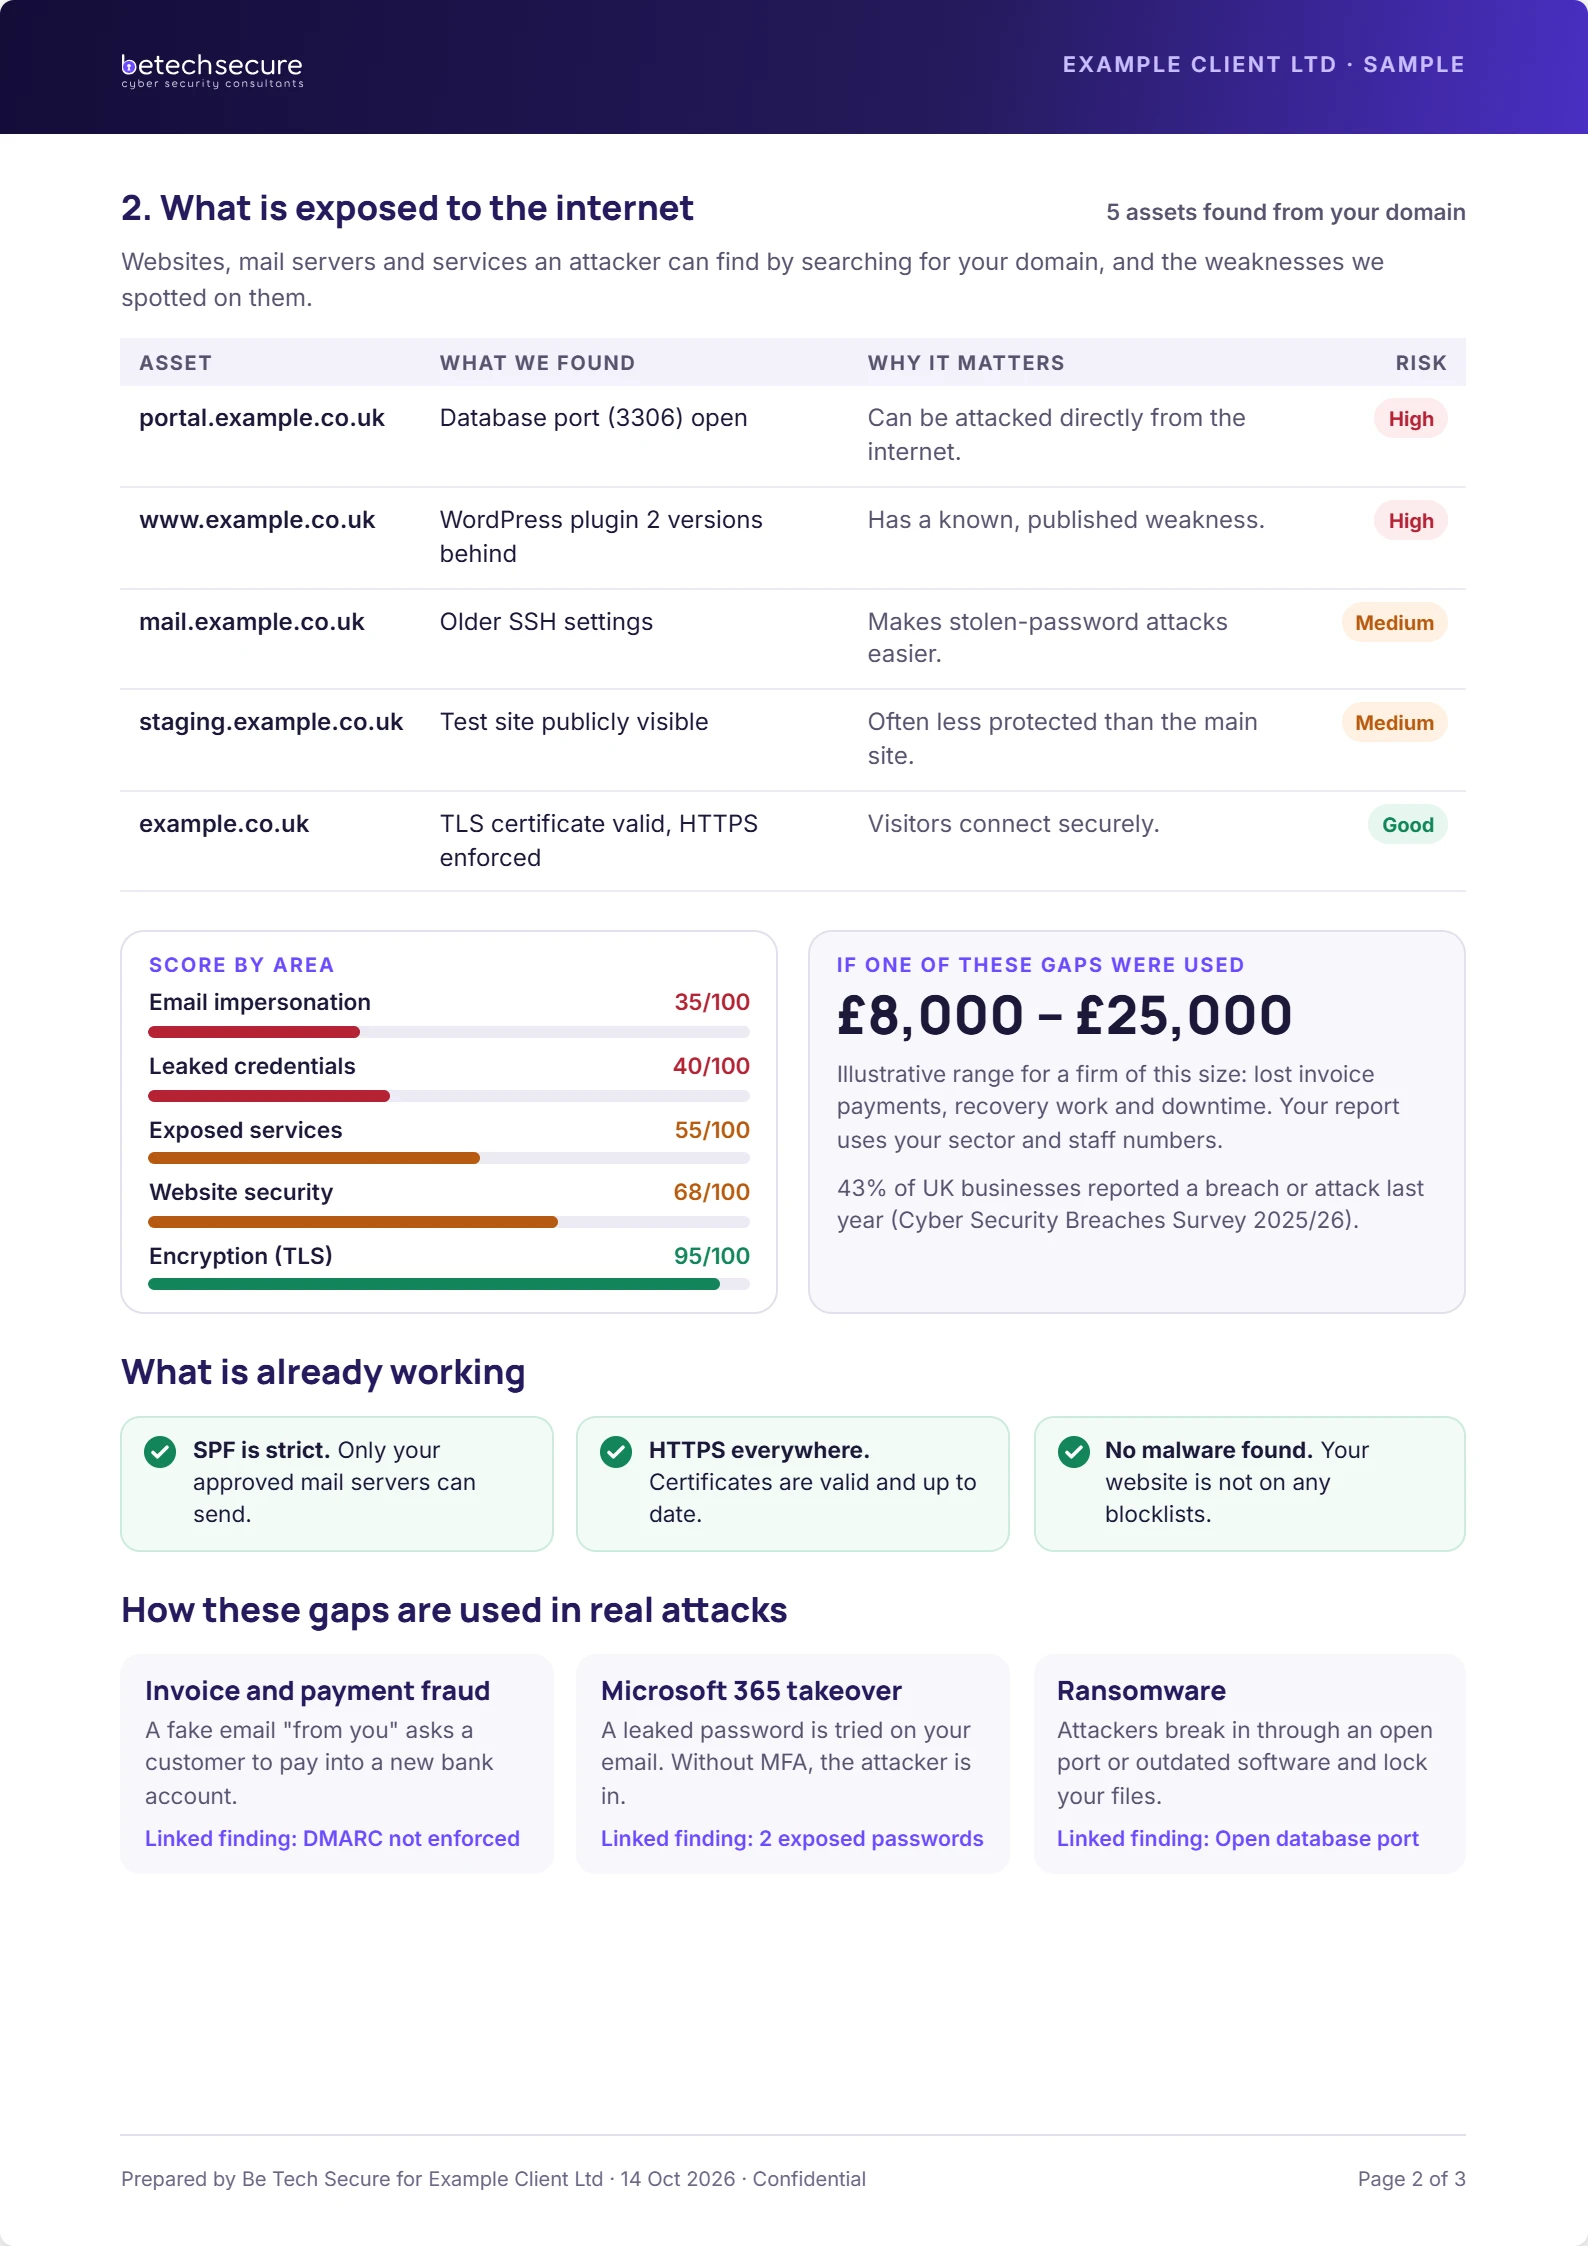
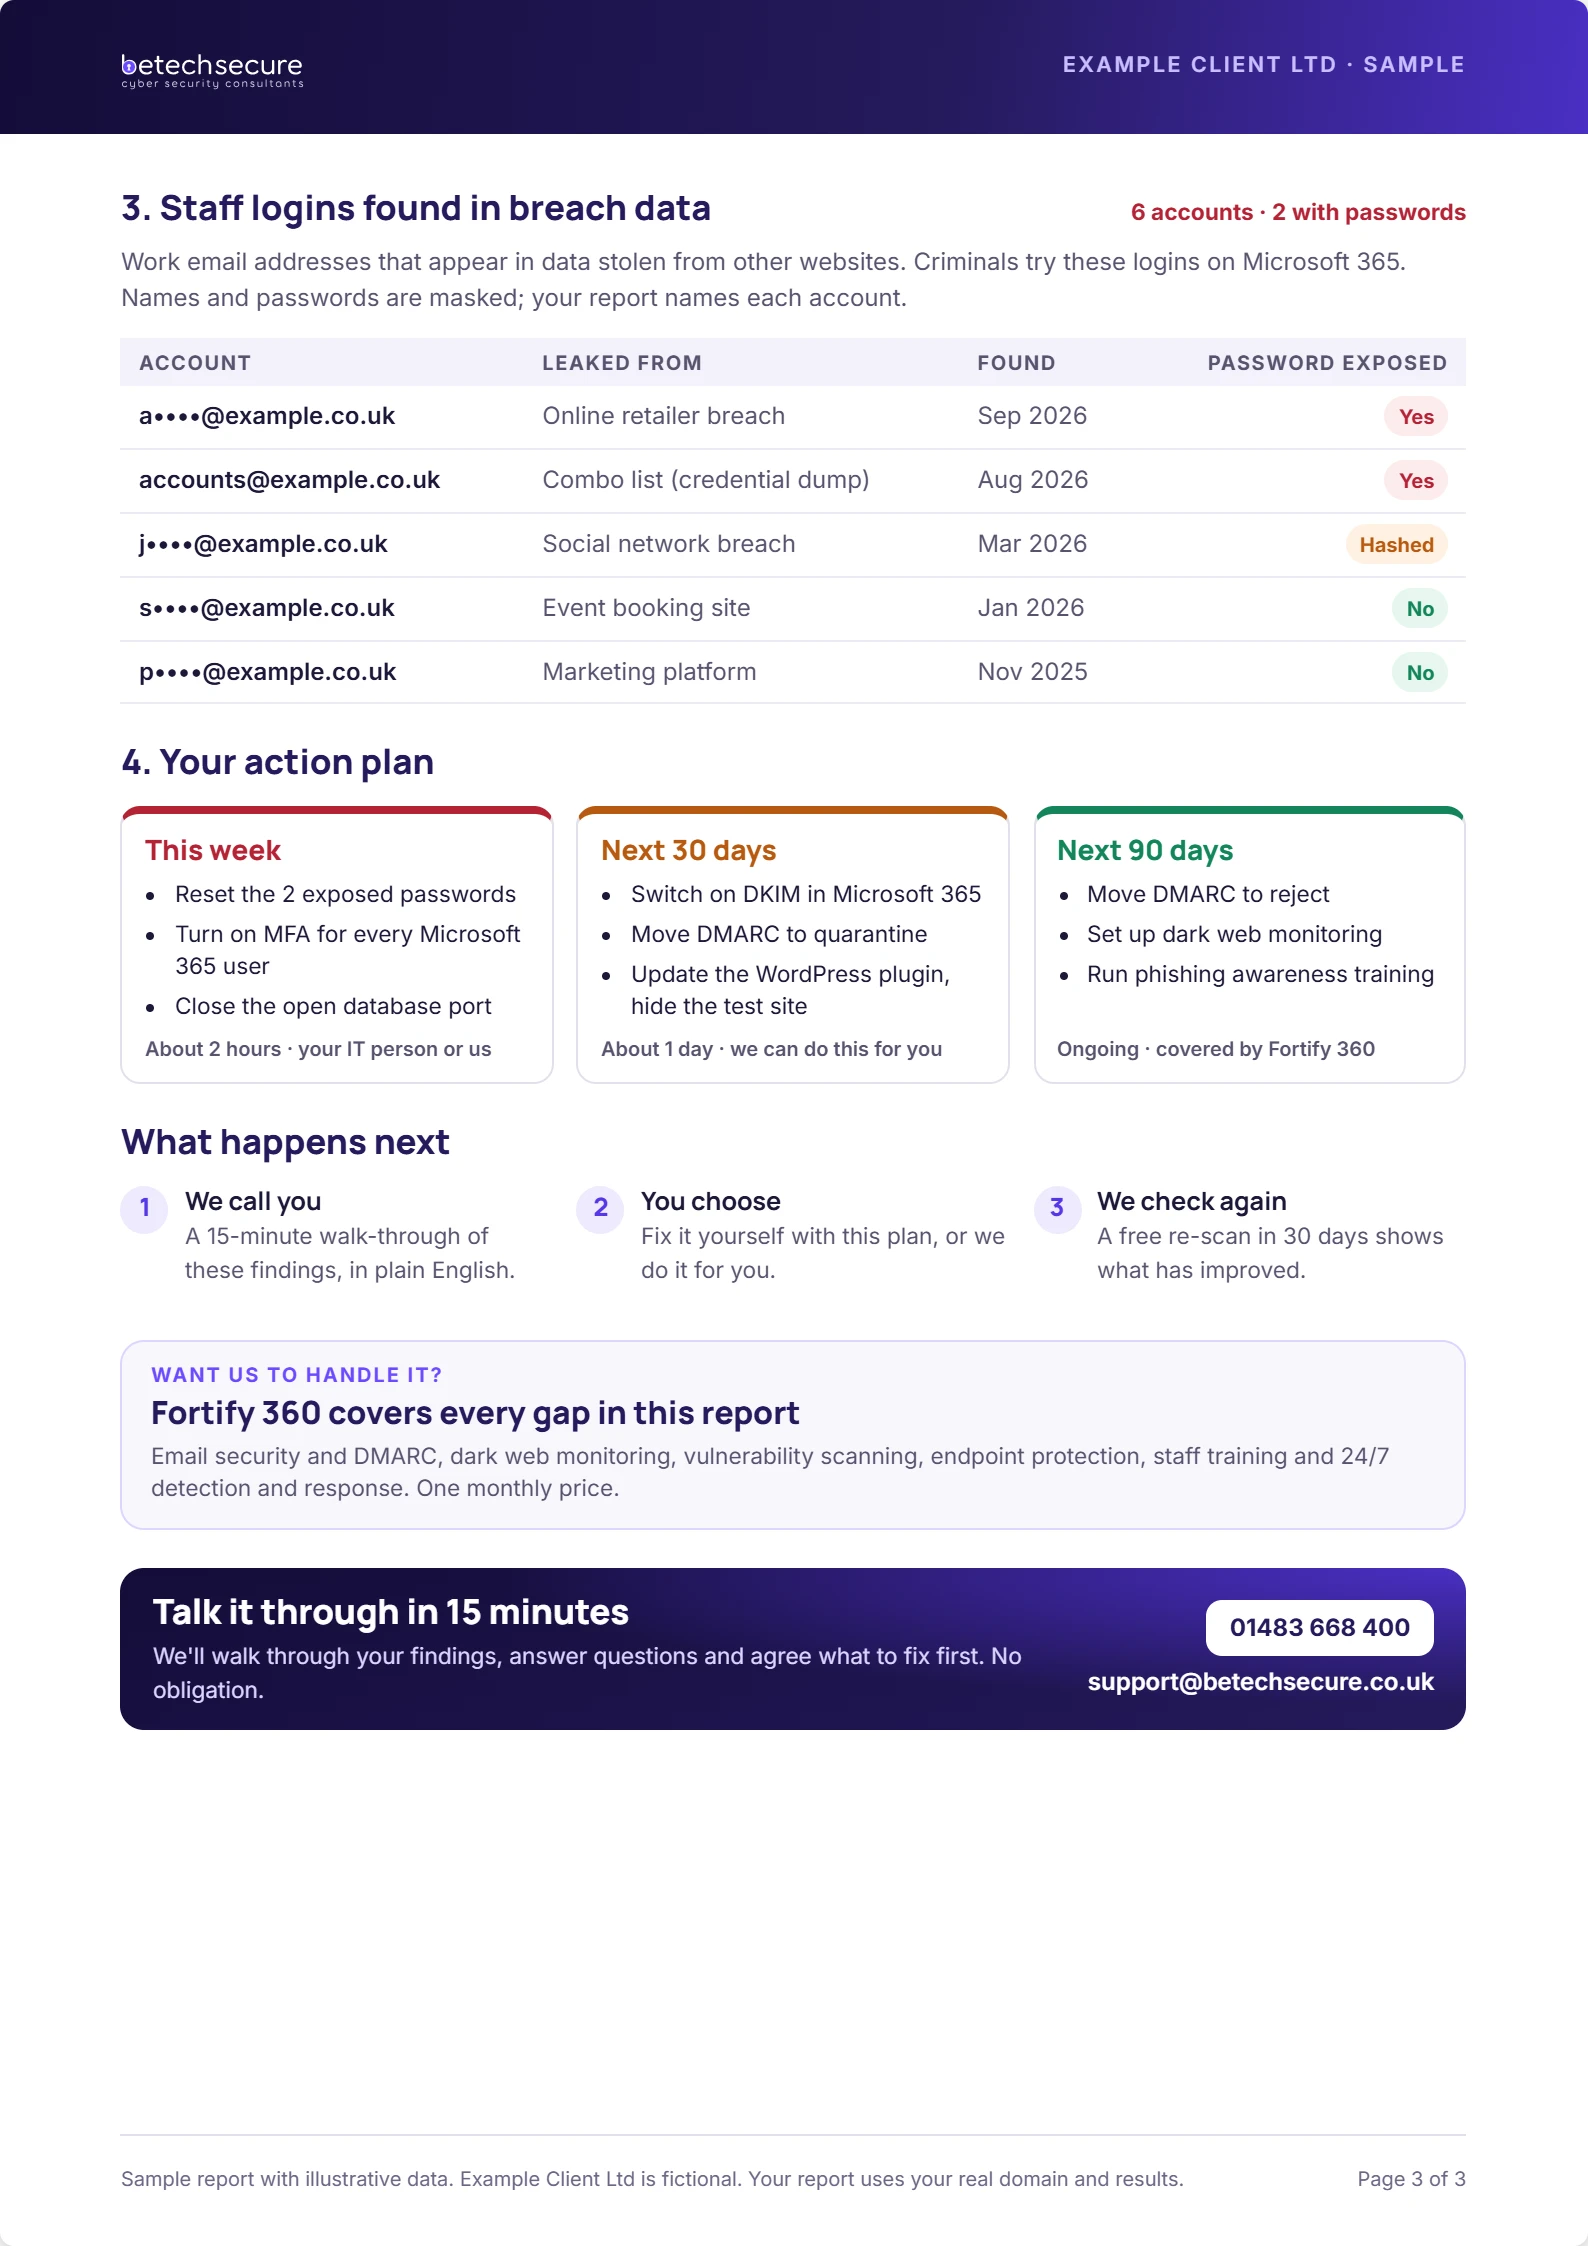
 Plus detailed technical findings, evidence and remediation steps
A report your board and your developers can both use
Every test ends with a clear, practical report and a debrief call, so you know exactly what to do next.
- Executive summary in plain English for leadership
- Technical findings with evidence and proof of concept
- Clear risk ratings to prioritise what matters
- Step-by-step remediation guidance
- Debrief call and optional retest
Real security experts. Not just automated scanning.
Our penetration testing is carried out by experienced security specialists who manually validate and safely exploit vulnerabilities to understand their real-world impact.
- CREST-accredited testing partner
- Experienced and certified security specialists
- Ethical, safe and professional approach
- Clear communication throughout
Find your weaknesses before attackers do
Get a fixed-price quote in 2 minutes, or book a free scoping call with a security specialist. Want ongoing protection afterwards? See Fortify 360.
- No obligation
- Fixed-price quotes
- UK-based experts
Penetration testing: frequently asked questions
Last reviewed October 2026 by the Be Tech Secure security team
A penetration test (pen test) is an authorised, simulated cyber attack on your systems, carried out by security specialists to find and safely exploit weaknesses before real attackers do. You get a report showing what was found, how serious it is and exactly how to fix it.
A vulnerability scan is automated and lists potential weaknesses. A penetration test goes further: experienced testers manually confirm and safely exploit vulnerabilities to show their real-world impact, and remove the false positives scans often produce.
It depends on the scope, such as the number of IP addresses, applications or users, and the type of testing. Complete our 2-minute quote form or book a free scoping call and you will get a clear, fixed quote with no hidden extras.
Most SME tests take between 2 and 10 days of testing, depending on scope. Your report is usually delivered within a week of testing finishing, and we can work to tender or audit deadlines.
No. Testing is planned around your business, with agreed rules of engagement and testing windows. Our testers use safe techniques and stop immediately if anything could affect live systems.
At least once a year, and after any significant change such as a new website, system migration or office move. Many customers, insurers and frameworks also expect annual testing.
Yes. Testing is delivered through a CREST-accredited testing partner by experienced, certified security specialists, so your report will be accepted by customers, insurers and auditors.
An executive summary for leadership, detailed technical findings with evidence, clear risk ratings and practical, prioritised recommendations, plus a debrief call to talk it through.
Yes. We can retest fixed vulnerabilities to confirm they have been resolved, giving you updated evidence for customers, insurers or auditors.
Cyber Essentials Plus includes its own technical audit, while ISO 27001 expects regular technical testing, which a pen test provides. Many businesses combine them, and we can help with both.
Not sure what type of test you need?
Tell our cyber security AI what you're trying to protect, or what a customer or insurer has asked for, and it'll help you define the right scope.