For FCA-regulated firms with 5–50 staff
Cyber security for financial advisers. Protect client money and data.
Stop payment fraud and email impersonation, protect client records, and evidence the systems and controls the FCA, platforms and insurers expect. Built for advisers, wealth managers and brokers.
- Stop payment fraud and email impersonation
- Protect client records and portfolios
- Detect and respond to threats 24/7
- Evidence FCA systems and controls (SYSC) and GDPR
“We needed confidence that our client data was protected and that our security arrangements could stand up to scrutiny.”
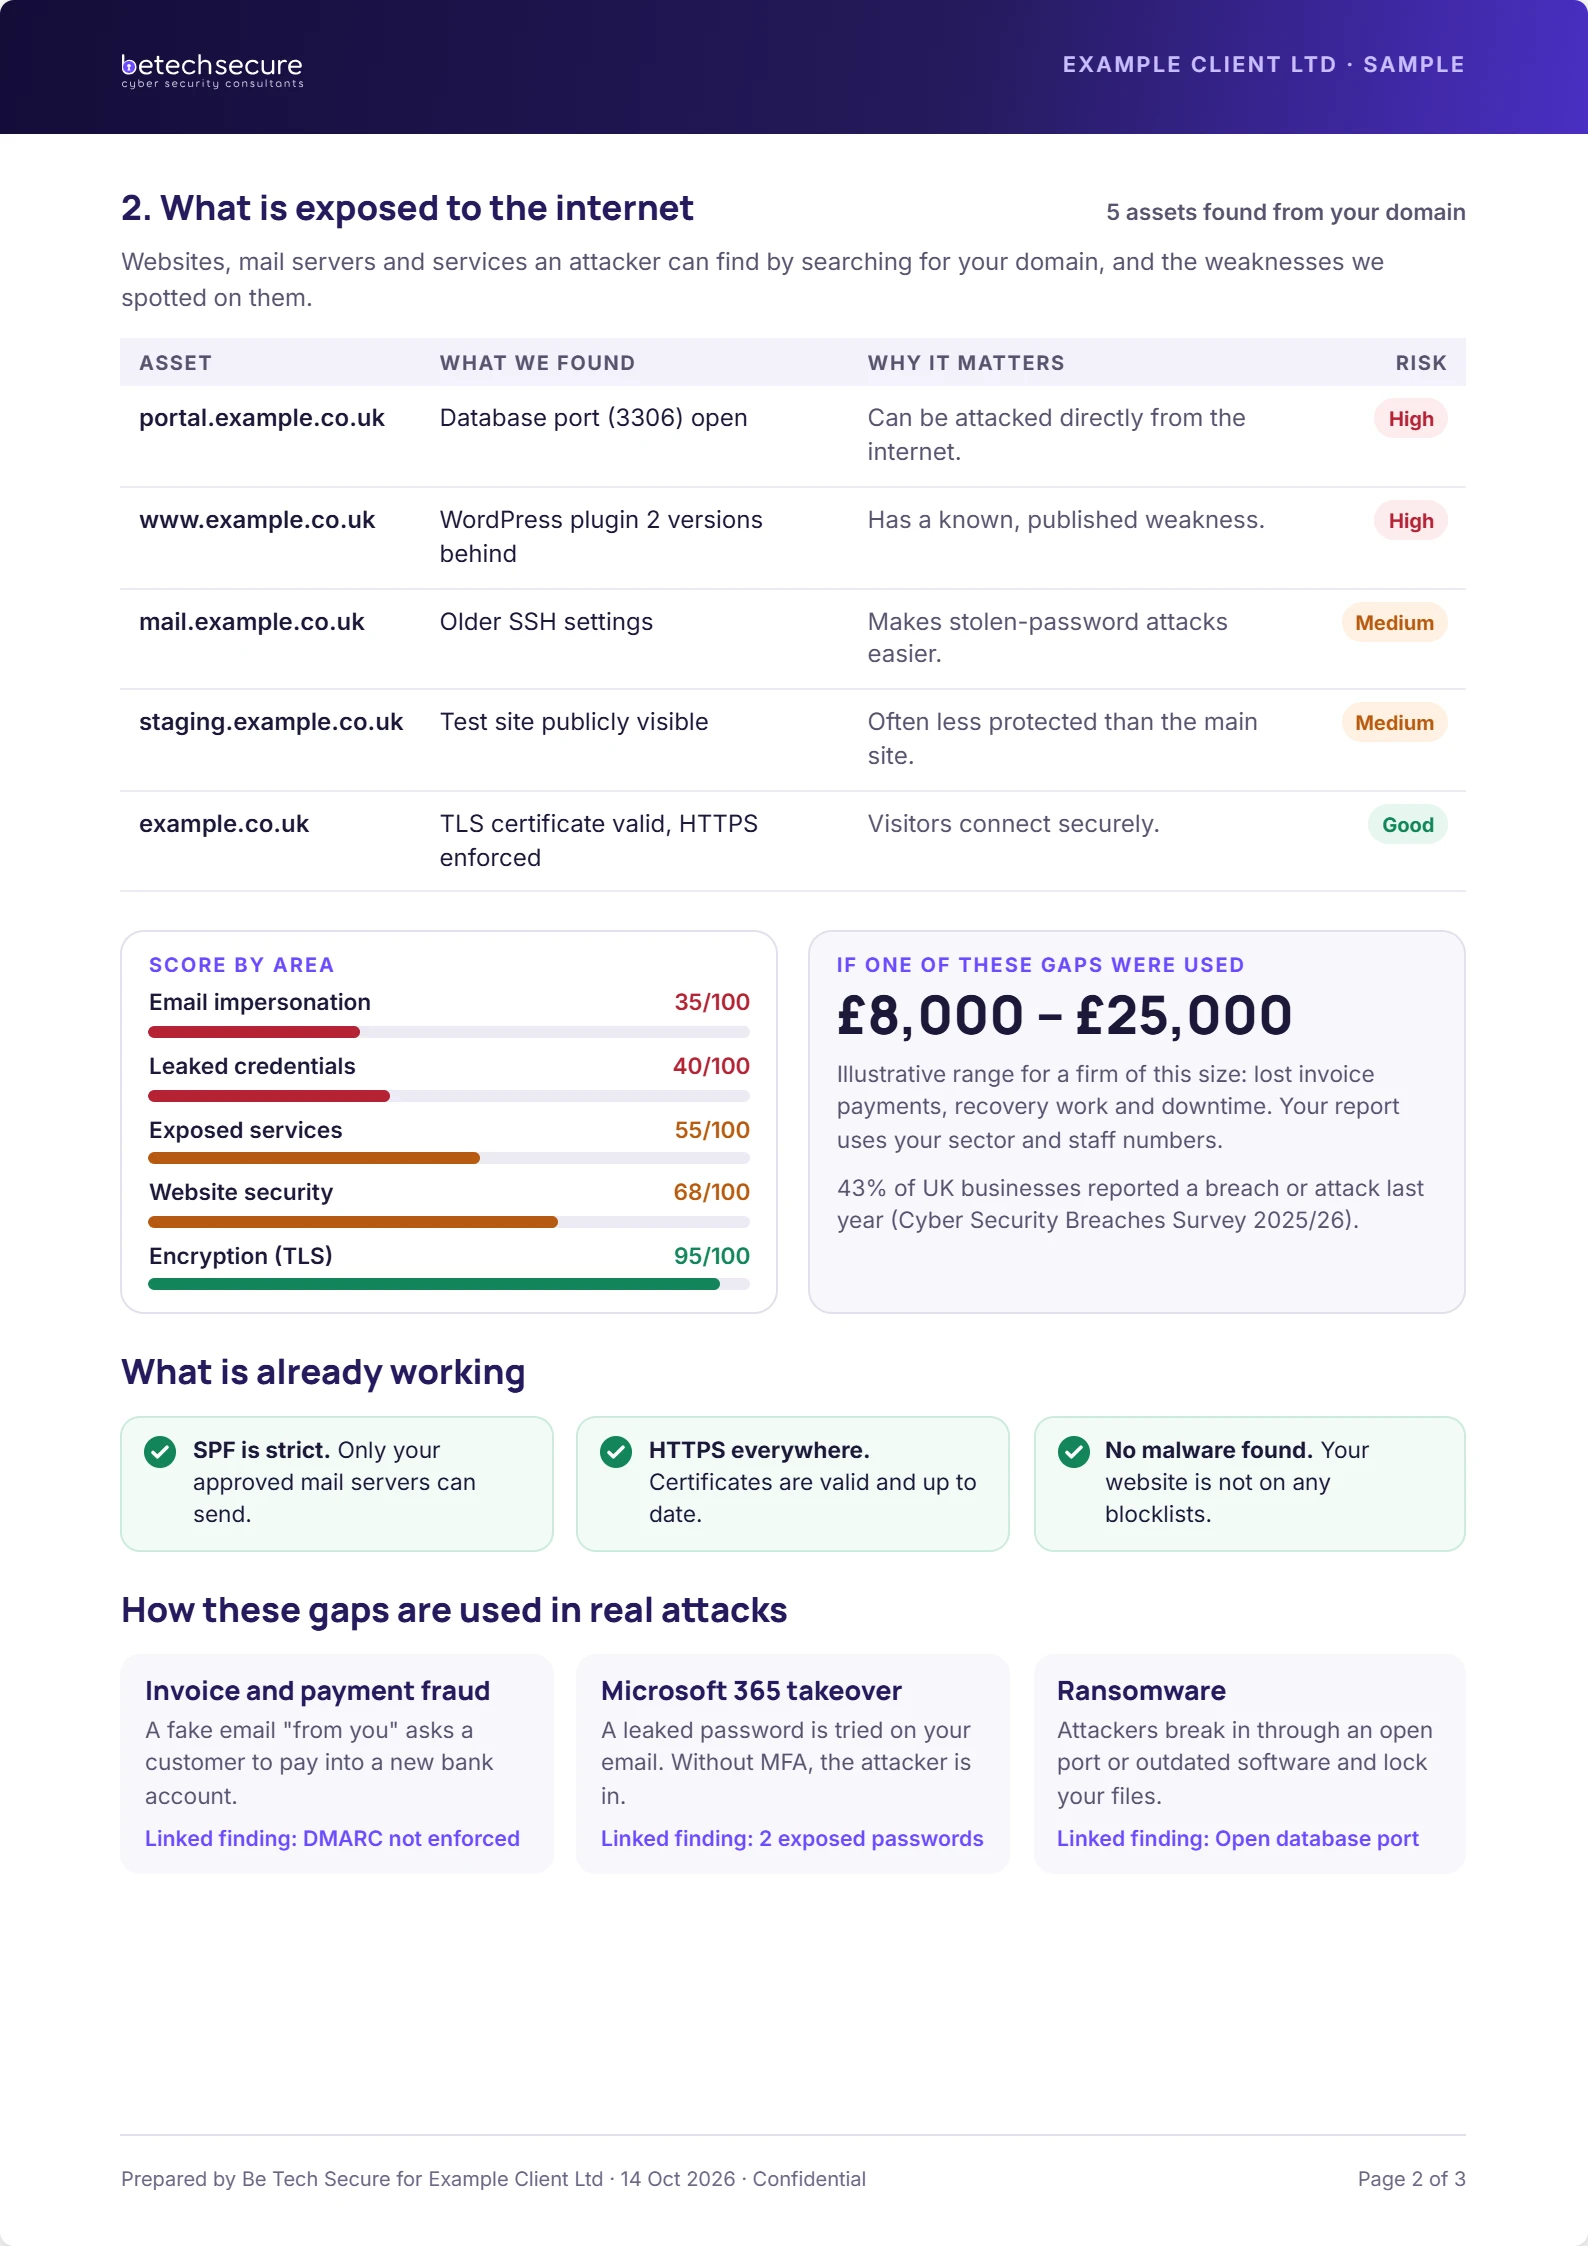
Your score updates live as you answer.
- 4 questionsabout 60 seconds
- Live scoreas you answer
- UK specialistreviews every report
Certifications & partnerships
The real cyber risks facing financial services firms
Financial firms hold money, data and trust, which makes them a high-value target.
Payment & transfer fraud
Criminals impersonate clients to request withdrawals or change bank details.
Business email compromise
One compromised mailbox lets attackers watch and hijack client conversations.
Client data theft
Personal and financial records are valuable and must be protected under GDPR.
Regulatory pressure
The FCA expects firms to manage cyber risk and operational resilience.
Third-party platforms
Platforms, back-office systems and suppliers can all introduce risk.
Ransomware & downtime
An attack can stop you advising clients and processing business.
Remote & hybrid advisers
Advisers working from home or client meetings need protected laptops and secure sign-in.
Insider & leaver risk
Departing staff can take client lists and data unless access is removed promptly.
How we protect financial services firms
Four stages, starting with the controls that stop money leaving the wrong way.
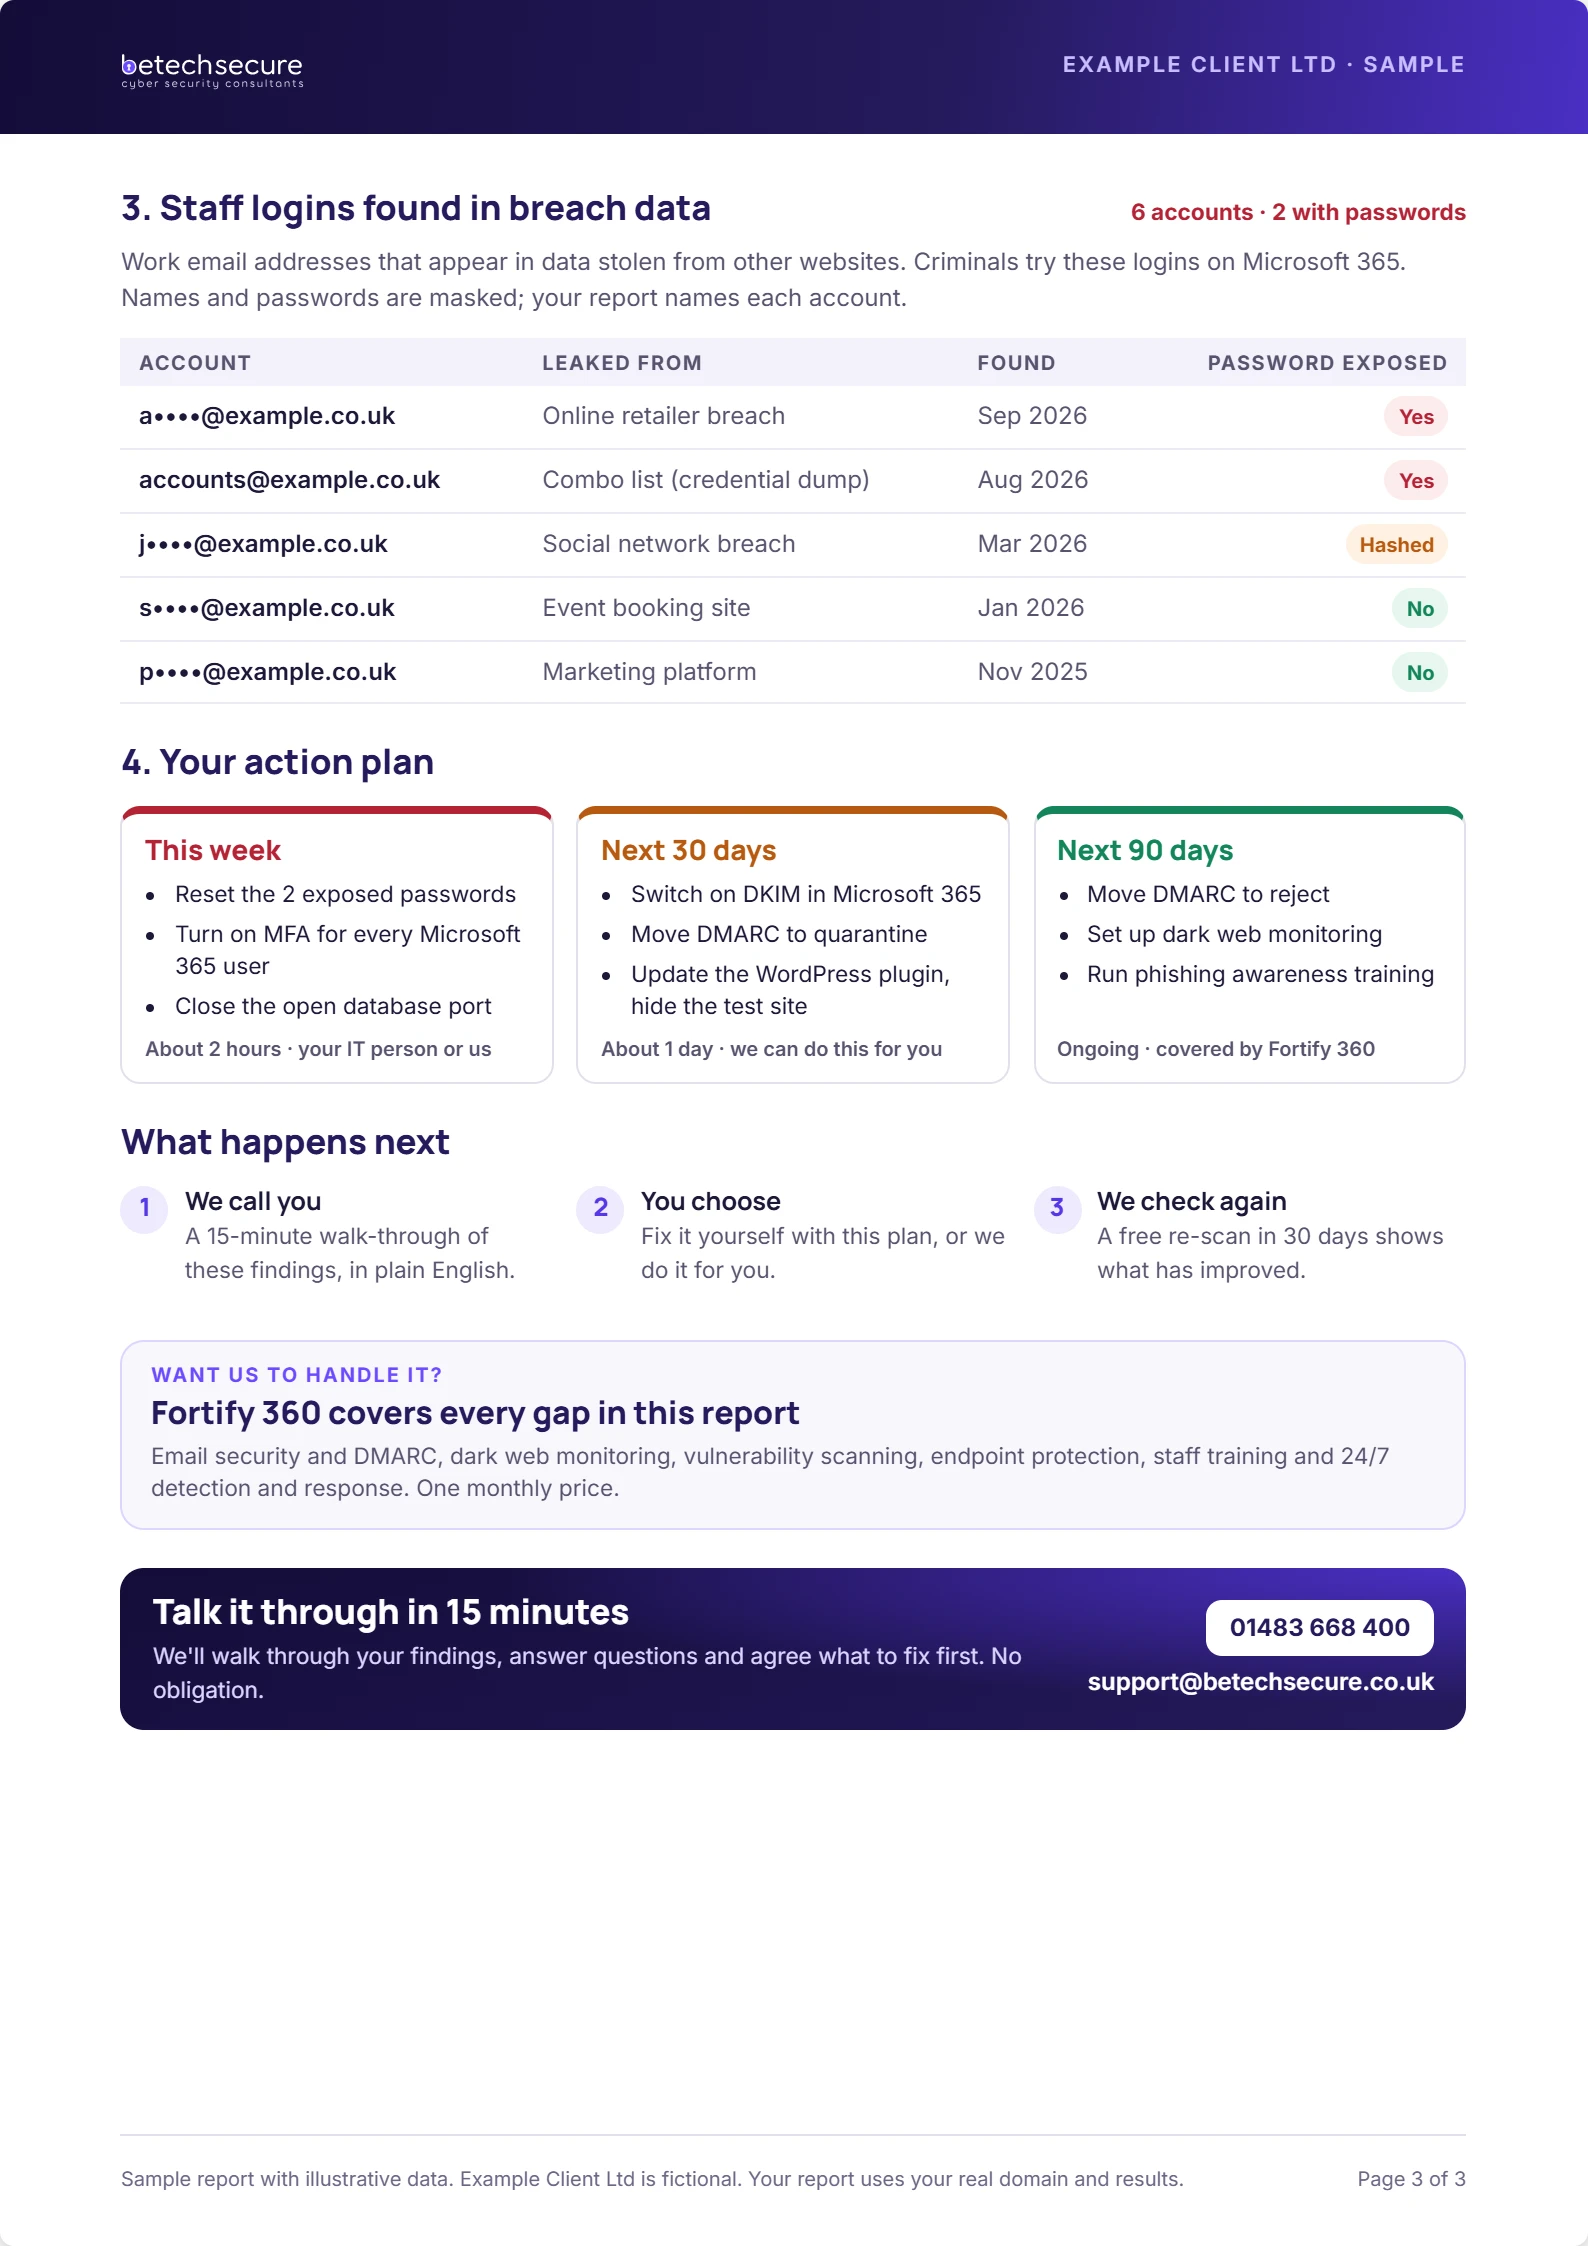
- 1Map how money movesWe trace how withdrawal and bank-change requests reach you, and where an attacker could step in.
- 2Lock down mailboxesMFA, impersonation filtering and DMARC so criminals cannot read or fake client conversations.
- 3Train the teamShort, regular training and simulated fraud emails for advisers and paraplanners.
- 4Evidence and monitor24/7 monitoring plus a security pack you can hand to platforms, insurers and compliance consultants.
Simple per-user pricing for adviser firms
Fortify managed security covers email, devices and accounts for every adviser and support colleague, with 24/7 monitoring and UK support.
- Fixed monthly price, agreed upfront
- No long-term contract
- Due diligence pack included
- No obligation
- Takes 60 seconds
- UK-based experts
Your IT provider keeps you running. We keep client money safe.
Most adviser firms already have IT support. We add the specialist fraud and security layer on top, agree who owns what, and report in plain English to the directors and compliance lead.
- No change of IT provider needed
- Named security contact for compliance
- Monthly report you can share with the board
- Help with platform and insurer questionnaires
Fewer fraud attempts reach your clients
Our cyber security solutions for financial services
Practical, outcome-focused solutions for regulated firms.
Protect accounts & email
Advanced email security, MFA and impersonation protection.
Learn more about Protect accounts & email24/7 threat monitoring
Continuous monitoring and rapid response to stop attacks early.
Learn more about 24/7 threat monitoringSecurity awareness training
Help advisers and support staff spot fraud and phishing.
Learn more about Security awareness trainingCompliance support
Cyber Essentials, ISO 27001 and evidence for client due diligence.
Learn more about Compliance supportPenetration testing
Independent testing of your systems and client-facing services.
Learn more about Penetration testingvCISO
Board-level reporting and a clear security roadmap.
Learn more about vCISO
Products we use to protect adviser firms
Each one is deployed, configured and managed by our UK team.
- Sendmarc DMARCStop criminals sending email as you
- Email SecurityBlock impersonation and phishing before it lands
- Endpoint Protection24/7 ransomware detection on every device
- TeramindSpot risky data movement and insider activity
- Cyber EssentialsIndependent proof for clients and insurers
- Free guides and checklistsPractical checklists and guides for your sector
What adviser firms say
What advisers and practice owners say after working with us.
“We handle sensitive financial information every day. Relying on antivirus alone no longer felt like enough protection for our business.”
24/7 managed threat monitoring introduced
Paul W.Managing Director · Financial Services, 18 staff“Client security questionnaires were becoming increasingly detailed. We needed help demonstrating that our controls were documented and properly managed.”
Improved security governance and questionnaire readiness
Charlotte D.Compliance Manager · Financial Services, 27 staff“We were concerned about unauthorised access to client emails and documents, especially with staff working across multiple locations.”
Stronger Microsoft 365 identity and access controls
Richard F.Operations Director · Financial Services, 23 staff
Free resources
Practical guides for financial services firms
Checklists and guides written for your sector. Free, instant access with your work email.
 ChecklistFinance: Client Money & Payment Fraud ChecklistControls that protect client money, payment approvals and FCA expectations.Get it free
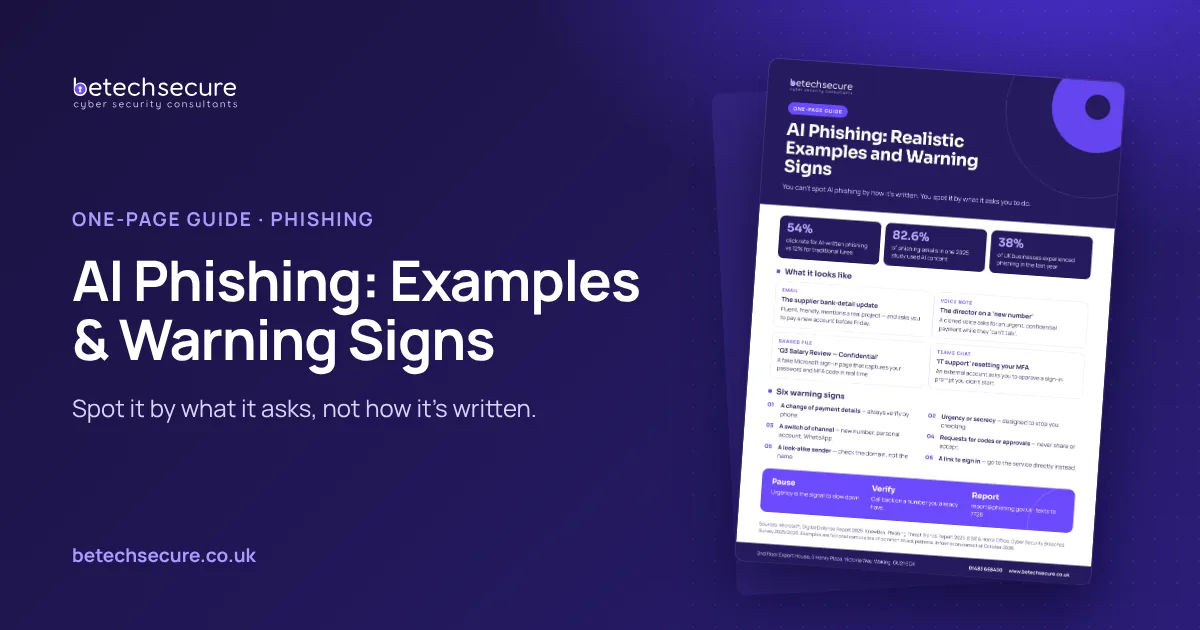 Visual guideAI Phishing: Realistic Examples and Warning SignsOne page for your team: what AI phishing looks like, six warning signs that still work, and what to do.Get it free
 Checklist5 Microsoft 365 Security Checks for SMEsFive checks that close the most common Microsoft 365 gaps, plus quick wins you can do this week.Get it free
Frequently asked questions
Last reviewed October 2026 by the Be Tech Secure security team
At minimum: MFA on every account, email impersonation protection, DMARC on your domain, managed antivirus with 24/7 monitoring, tested backups and regular staff training. Add a written call-back rule for any change of bank details. Cyber Essentials proves these basics to platforms and insurers.
The PS21/3 operational resilience rules apply to banks, insurers, payment firms and enhanced-scope SM&CR firms. Most small advisory firms are outside their scope, but SYSC still requires adequate systems and controls, and Consumer Duty expects you to prevent foreseeable harm to clients, including fraud. We help you evidence both. We do not give regulatory advice.
Usually by compromising or faking a mailbox. They watch real conversations, then send a withdrawal or bank-change request that looks genuine. MFA, impersonation filtering, DMARC and a call-back rule on a known number stop most attempts.
Yes. We combine email security, domain protection, MFA and staff training to reduce the risk of impersonation and payment diversion.
DMARC tells receiving mail servers to reject email that pretends to come from your domain. Without it, anyone can send convincing emails to your clients as your firm. We set it up and take you to full enforcement with Sendmarc.
Yes. Our vCISO and compliance services can plan, lead and support your journey to certification.
Usually proof of MFA, endpoint protection, backups, staff training and an incident response plan, and often Cyber Essentials. We provide a security pack with this evidence and help you complete questionnaires.
Yes. We work alongside your IT provider or internal team, adding specialist cyber security with clear responsibilities agreed from day one.
Most firms are protected within two to four weeks, starting with the highest-risk areas first.
Fortify managed security is a fixed monthly price per user, so costs are predictable and grow with your team. The price depends on how many people you have and which services you need. We confirm a fixed quote after a free 15-minute call, with no long-term contract.
Find out how exposed your firm is
Get your live risk score in 60 seconds, or book a 15-minute call with a UK specialist who works with adviser firms.
- No obligation
- UK-based experts
- Clear, practical advice